Your security manager reviews the risk register on Monday. Wednesday brings a revision to a cloud access policy by a developer. On Friday, someone uploads a revised security procedure, yet the Statement of Applicability still references the earlier version.
Nothing especially alarming has happened. Yet these everyday mismatches can create serious difficulties when an ISO 27001 auditor starts examining the documentation. The difficulty for a startup is maintaining consistent documentation without taking attention away from the business.
When Spreadsheets Start Taking Over Your Workday
For many teams, spreadsheets offer a simple and inexpensive way to organize information. However, spreadsheets can be accidentally overwritten without anyone noticing. A growing business may begin with separate trackers for risks and control responsibilities. That arrangement can work while the project is relatively simple, but problems appear when responsibilities shift or several employees make independent updates.
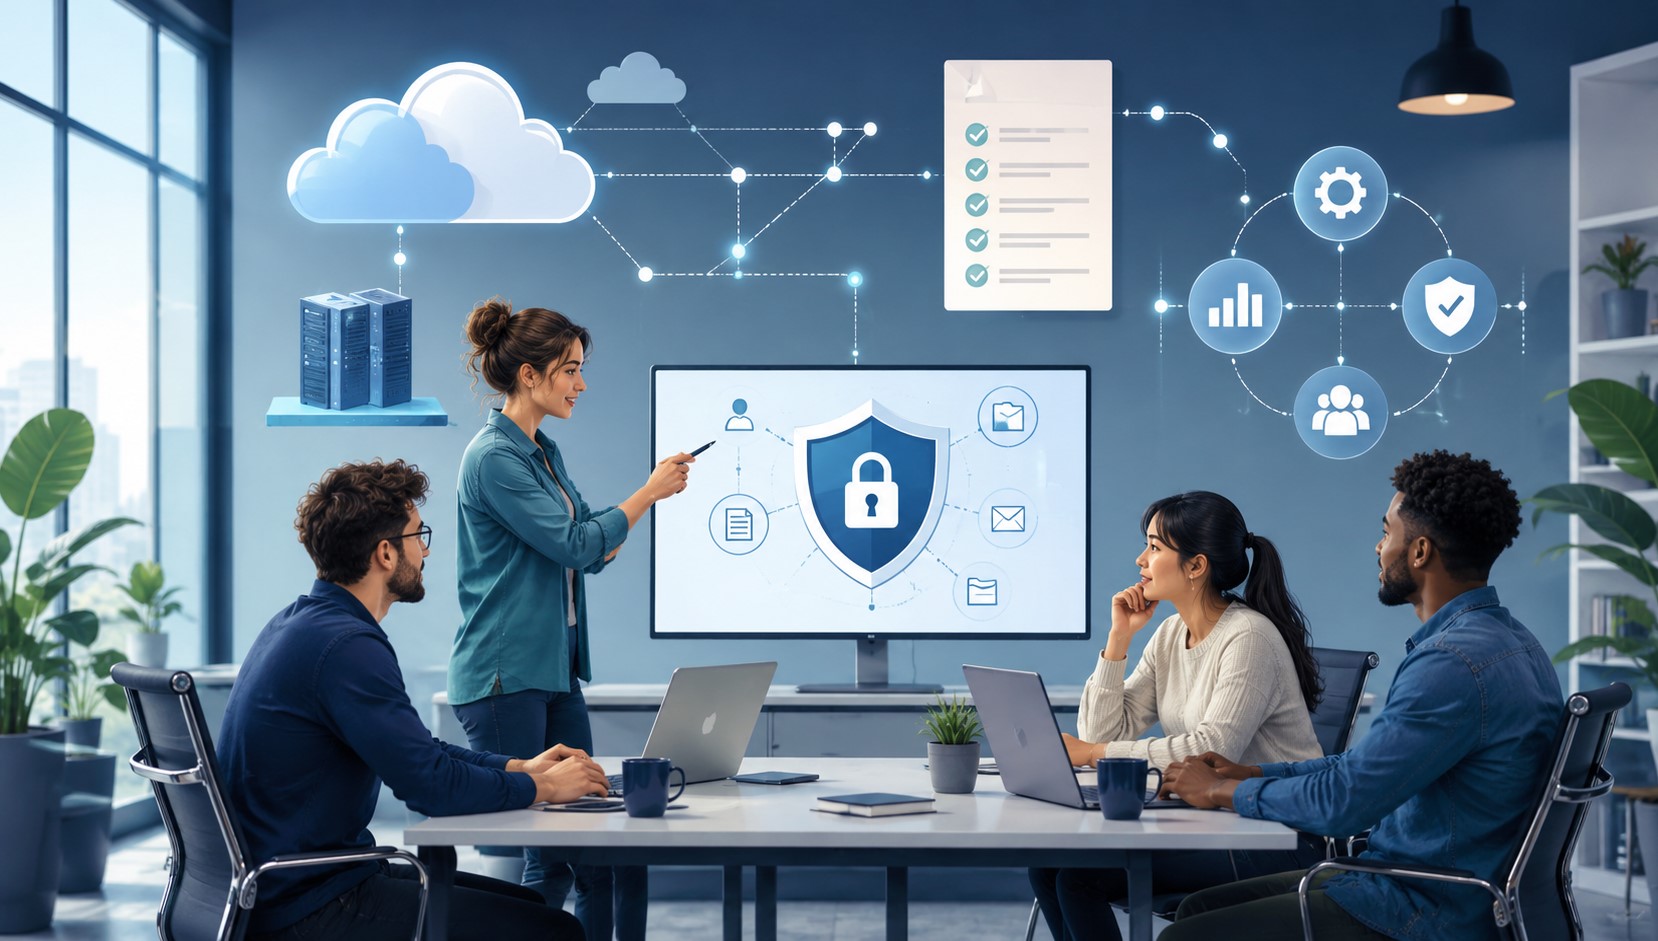
ISO 27001 compliance software can replace this fragmented process by bringing related activities into a structured workspace. A shared workspace makes it easier to review control documentation and status together in one place.
What Startup Leaders Need to Know
Before committing to a platform, founders should consider who will own its ongoing administration.
A startup with eight employees probably does not need the same compliance infrastructure as a multinational organization. In a small team, risk assessments may fall to founders, technical controls to developers, and documentation to a designated coordinator.
A useful ISO 27001 software platform makes responsibilities visible without unnecessary complexity. If employees are reluctant to update a system, its tools are unlikely to deliver much practical benefit.
Why the Statement of Applicability Matters
The Statement of Applicability serves a purpose greater than collecting signatures. It explains which security controls an organization considers necessary, why those controls were selected, and whether they have been implemented.
Using cloud infrastructure does not remove the need to consider applicable physical security responsibilities, even when the provider manages the underlying buildings.
The business should maintain clear documentation of its responsibilities and control decisions. Linking the risk register with the Statement of Applicability helps an auditor trace control decisions to risks.
What Should You Expect During an Audit?
During an assessment, an auditor might request access records, training evidence, security policies, and risk treatment decisions. A fragmented filing process can make it slower to gather audit materials. ISO 27001 certification software helps organize these materials, but it does not guarantee that the evidence is sufficient or that certification will be granted.
An accredited certification body independently evaluates whether the information security management system satisfies the applicable requirements. Keeping records clear and accessible helps the team prepare evidence more efficiently.
A More Manageable Approach for Startups
When evaluating software, startups need to weigh cost, staff capacity, and the compliance work they genuinely need to manage. CertAssist offers a practical option for businesses searching for the best compliance software for startups ISO 27001 certification. CertAssist brings together a risk register, a Statement of Applicability, editable policy guidance, evidence storage, ISO 27001 clauses, and Annex A controls.
Auditors can be given direct access, and the platform does not require integration with company infrastructure. That can be helpful for businesses that prefer managing evidence themselves.
How to Prevent Compliance From Becoming a Bottleneck
Certification preparation should not prevent employees from focusing on customers, product development, and daily operations. A manageable system supports up-to-date evidence, visibility into incomplete work, and preparation for an independent audit.
CertAssist aims to give smaller businesses the organization needed for ISO 27001 work without excessive administrative complexity. A long feature list is not, by itself, proof of usefulness. A useful platform is one that allows the business to keep records consistent as its needs evolve.